The 3-2-1 backup rule means keeping three copies of your data, on two different types of storage, with one copy stored off-site. It is the simplest backup plan that actually works, and it is the plan recommended by the US Cybersecurity and Infrastructure Security Agency (CISA) for small businesses. This guide explains the rule in plain English, shows what it looks like for a five-person UK firm, and covers what it costs per year.
Most small firms do not lose data because they never thought about backups. They lose data because they had one backup, and that one backup failed, was encrypted, or sat in the same building as the original. The 3-2-1 rule fixes that with simple arithmetic.
The rule in 30 seconds
The rule has three numbers, and each number answers one specific failure.
Three copies. Keep the original data plus two backups. One backup is a spare. Two backups mean you still have a spare while one copy is being restored or repaired.
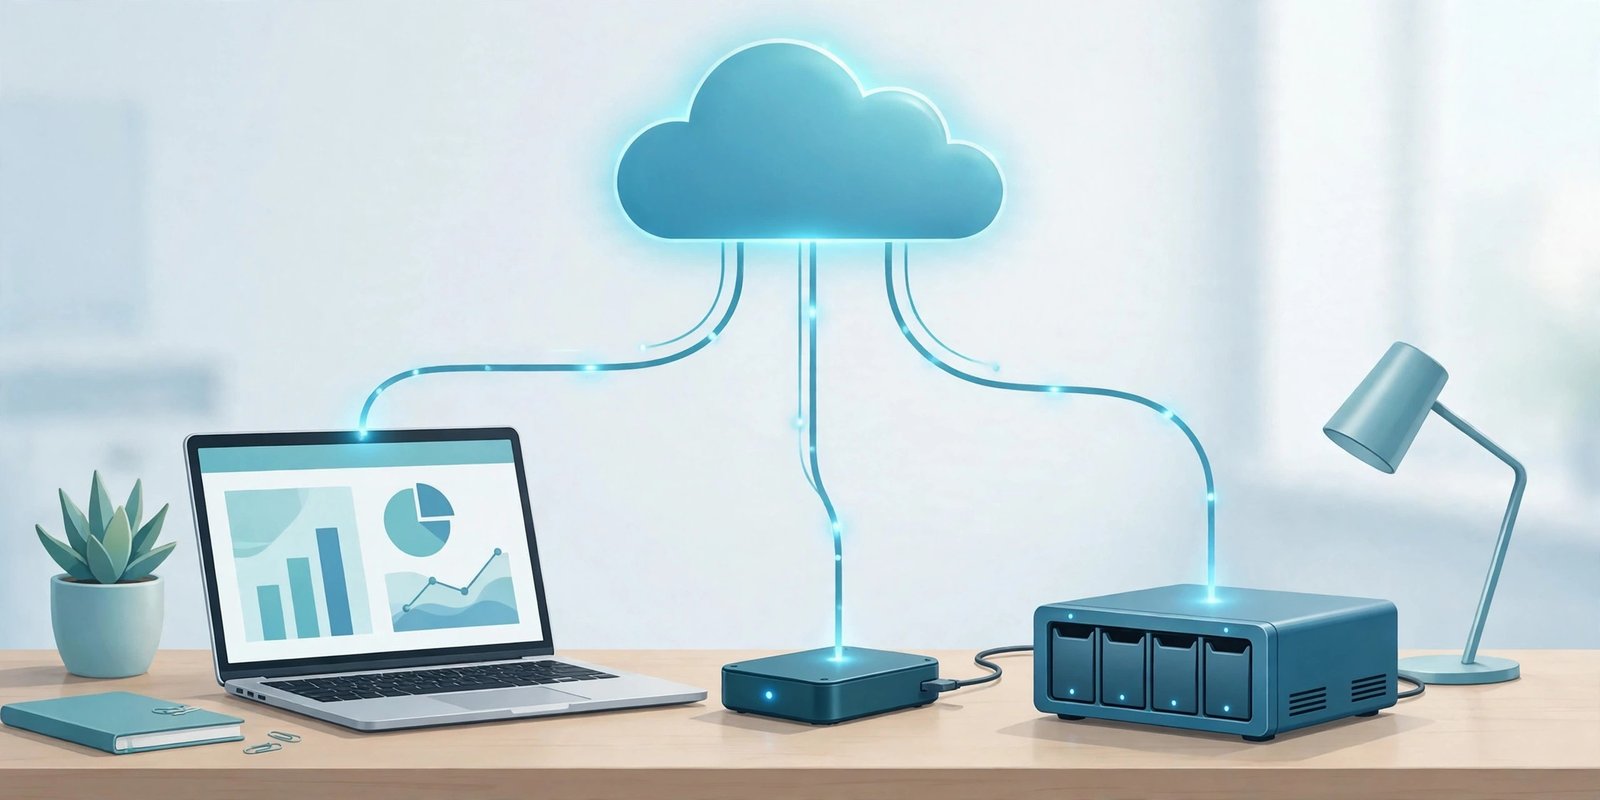
Two types of storage. Keep the copies on different kinds of storage, for example a laptop plus an external hard drive, or a NAS drive plus a cloud backup service. If one storage type fails, or one system is attacked, the other type survives.
One copy off-site. Keep at least one copy in a different physical location from your office. Fire, flood, theft and a burst pipe can all destroy everything in one building at once. An off-site copy survives the loss of the building itself.
The rule dates back to photographer Peter Krogh, who described it in his book The DAM Book. It is still the standard today because no single event, whether a failed drive, a deleted folder or a ransomware attack, should be able to reach every copy you have.
A worked example for a five-person firm
Imagine a small UK firm with five staff, working from laptops and Microsoft 365. Here is what 3-2-1 looks like for them, with no IT department and no server room.
| Copy | Where it lives | What it holds | How often it updates |
|---|---|---|---|
| Copy 1 (live data) | Laptops and Microsoft 365 | Working files, email, invoices, customer records | Constantly, as staff work |
| Copy 2 (local backup) | A NAS drive or external hard drive in the office | A full backup of every laptop and the shared folders | Every night |
| Copy 3 (off-site backup) | An encrypted cloud backup service | The same full backup, stored in a UK or EU data centre | Every night |
Start by listing the data the business cannot operate without, then back that up first. For most small firms the list is short: customer records, invoices and accounts, email, the website, and any files that would take days to rebuild. The UK National Cyber Security Centre (NCSC) gives the same advice in its guidance for small organisations: make a copy of all the data your business needs to operate, and work from that list.
A five-person firm can set this up in an afternoon. Install a cloud backup service on each laptop, plug in a NAS drive or an external hard drive, and schedule a nightly backup. The hard part is not the setup. The hard part is testing that the restore works, which we cover below.
What counts as each copy
Not everything that looks like a copy counts. These are the common traps.
A second folder on the same drive does not count. If the drive fails, both copies go together. A copy must live on separate storage.
Sync is not backup. OneDrive, Dropbox and Google Drive mirror your files. Delete a file, or encrypt it with ransomware, and the change syncs to every device within minutes. Sync keeps files handy. It does not protect them. Microsoft’s own terms for Microsoft 365 recommend that you back up your content, because the service itself is not a backup.
RAID is not backup. A NAS drive with mirrored disks protects you against one disk failing. It does not protect you against a deleted file, a ransomware attack or a fire, because the same data sits on both disks.
A copy in the same office is not off-site. A second hard drive on the desk next to the first one is a local copy, not an off-site copy. Off-site means a different building, or a cloud service in a data centre elsewhere.
What does count as a second type of storage? A laptop plus an external hard drive counts. A NAS plus a cloud backup counts. Two cloud services in different accounts also count, as long as one cannot be reached from the other.
How often each copy should update
A backup is only as fresh as its last run. Match the schedule to how much work you can afford to lose.
Live business data: daily. Invoices, customer records, email and working documents should back up every night at least. If your firm takes orders or updates records all day, use continuous backup, where files copy within minutes of changing.
Local copy: nightly. A nightly backup to the office NAS or external drive gives you fast restores. A single deleted file comes back in minutes from a local copy.
Off-site copy: nightly. The cloud copy should run on the same schedule as the local one. There is no point in an off-site copy that is a month out of date when the office burns down.
There are two terms worth knowing. A full backup copies everything. An incremental backup copies only what has changed since the last backup, which is much faster. Most small firms run one full backup a week, then incremental backups every night. Versioning means the backup service keeps older versions of each file, so you can recover the version from last Tuesday, not just the latest one. Turn versioning on, and keep at least 30 days of versions.
How long should you keep backups? A common pattern for a small firm is daily backups kept for 30 days, weekly backups kept for three months, and monthly backups kept for a year or more. Ransomware can lie dormant for weeks before it strikes, so a short retention window can leave you with only encrypted copies. Some sectors have legal retention rules, so check yours before deleting old backups.
Testing your restore (the step everyone skips)
A backup you have never restored from is a hope, not a plan. The NCSC and CISA both say the same thing: test the recovery process on a regular schedule. Most firms never do, and they discover the problem on the worst possible day.
Run a restore test once a month. Pick a random file, or a random folder, and restore it to a test location. Time how long it takes. Write the time down. Then try a bigger test once a quarter: restore a whole laptop, or a whole shared folder, to a spare machine.
Check three things each time. First, does the file open? A backup can be corrupt without any warning. Second, is it the right version? Check the date on the restored file against the date you expected. Third, how long did it take? If a full restore takes two days, that is your real recovery time, and you should plan around it.
If you use a cloud backup service, check that the restore works from a different network and a different device. A restore that only works from the office computer is no help if the office is closed. Keep the test simple, keep a one-page note of what you did, and put the next test in the calendar before you forget.
Our WordPress security checklist for small business makes the same point for websites: backups you can actually restore are the whole point, and the checklist shows how to set them up.
What it costs per year
The 3-2-1 rule is cheap for a small firm. These are approximate prices as of November 2026, and they vary by supplier.
| Item | Typical cost |
|---|---|
| Cloud backup service, five users | £300 to £600 per year |
| External hard drive or NAS drive (one-off) | £60 to £400, depending on size |
| Backup software, if not included | £0 to £100 per year |
| Total, first year | About £400 to £900 |
After the first year the cost drops, because the hardware is already bought. Compare that with the cost of losing your data. Rebuilding customer records, reissuing invoices and recreating a website takes weeks, and some of it can never be rebuilt at all. For most firms the yearly backup bill is less than one day of lost trading.
Common mistakes
Only one copy. A single external drive is a single point of failure. If that drive fails, or is stolen with the laptop, there is nothing left.
Mistaking sync for backup. OneDrive and Dropbox are useful, but they are not backups. A deleted or encrypted file syncs everywhere, including to your supposed safety net.
Never testing a restore. Backups fail silently. Drives corrupt, cloud accounts lapse, and backup jobs stop running without an alert. Test monthly.
Keeping every copy on the same network. If ransomware reaches your office network, it will encrypt every drive it can see, including the backup drive plugged into the same computer. At least one copy must be somewhere an attacker cannot reach, which is why the off-site copy matters, and why an offline or immutable copy is even better.
Forgetting phones and laptops. Staff keep contacts, photos of receipts and messages on their phones. If the backup plan covers only the office computers, half the firm’s data is unprotected.
No passwords or encryption on backups. A backup drive holds everything, so it is the most valuable thing a thief can steal. Encrypt the backup and protect the cloud account with two-factor authentication.
The ransomware upgrade: 3-2-1-1-0
The classic rule is still right, but ransomware has changed the threat. Attackers now target backups deliberately. Sophos reports that 94% of ransomware victims had attackers attempt to compromise their backups, and 57% of those attempts succeeded. A firm can follow the 3-2-1 rule to the letter and still lose everything if its backups are reachable.
That is why many experts now extend the rule to 3-2-1-1-0. The extra 1 means at least one copy is offline or immutable, which is a copy that cannot be changed or deleted until a set time has passed, even by someone with your password. The 0 means zero errors when you verify your recovery, because an untested backup is not a backup.
For a small firm, the simplest way to add the extra 1 is an external hard drive that you disconnect after each backup, or a cloud backup service with immutability switched on. Either way, the point is the same: one copy must be out of reach of an attacker who has your credentials.
Ransomware usually gets in through a phishing email, so the backup plan sits next to the phishing plan. Read our guide on how to spot a phishing email to see the red flags, and if the worst has already happened, our guide on what to do after clicking a phishing link walks through the first steps.
Frequently asked questions
Is cloud backup alone enough?
No. Cloud backup is an excellent off-site copy, but it is still only one copy. If the cloud account is hacked, the subscription lapses, or the service has an outage, you have nothing else. Pair it with a local copy, and keep the cloud account protected with a strong password and two-factor authentication.
How long should I keep backups?
Keep daily backups for at least 30 days, weekly backups for three months, and monthly backups for a year or more. Ransomware can hide for weeks before it activates, so a short retention window can leave you with only infected copies. Check whether your sector has legal retention rules before you delete anything.
What about ransomware?
The 3-2-1 rule protects you against ransomware only if at least one copy cannot be reached by the attacker. Keep one copy offline or immutable, and test your restore regularly. The Cyber Security Breaches Survey 2025 found that around four in ten UK businesses identified an attack or breach in the previous year, so this is a mainstream risk, not an edge case.
Does the rule apply to a one-person business?
Yes, and it is even simpler. Your live copy is your laptop. Your second copy is an external hard drive. Your third copy is a cloud backup service. Set all three to run automatically, test a restore once a month, and you are covered.
Conclusion
The 3-2-1 backup rule is three copies, two types of storage, one copy off-site. It costs a small firm a few hundred pounds a year, it takes an afternoon to set up, and it is the difference between a bad day and a closed business. Set it up this week, test a restore this month, and put the next test in the calendar. Your future self will be glad you did.